Auckland Startup Week is a good reminder of something we see often in the Kiwi startup community. Security is on founders' minds, but it rarely makes it to the top of the list.
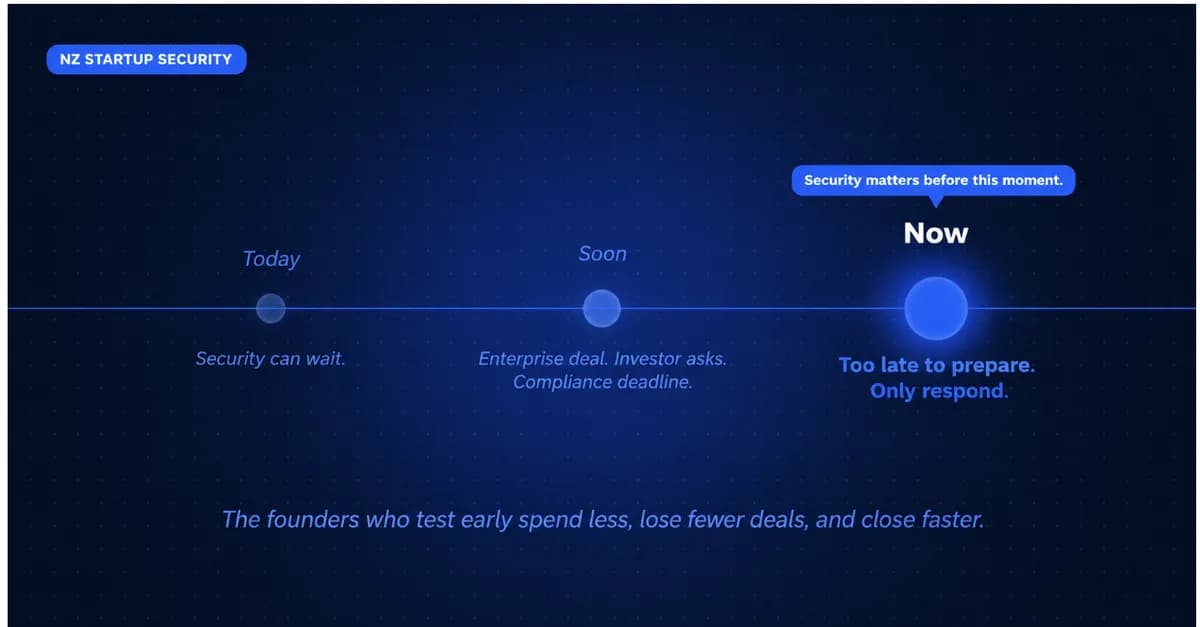
There is always a product to ship. A customer to close. A hire to make. Security feels like something you do later, once the budget is bigger and the team is more settled.
The problem is that later often arrives as a breach, a stalled enterprise deal, or a compliance deadline with no evidence to show.
Security matters most before those moments, not after them.
What NZ Founders Tell Us
Through our partnerships with Airtree and Ministry of Awesome, we have worked with startups at different stages across New Zealand and Australia. A few things come up in almost every conversation.
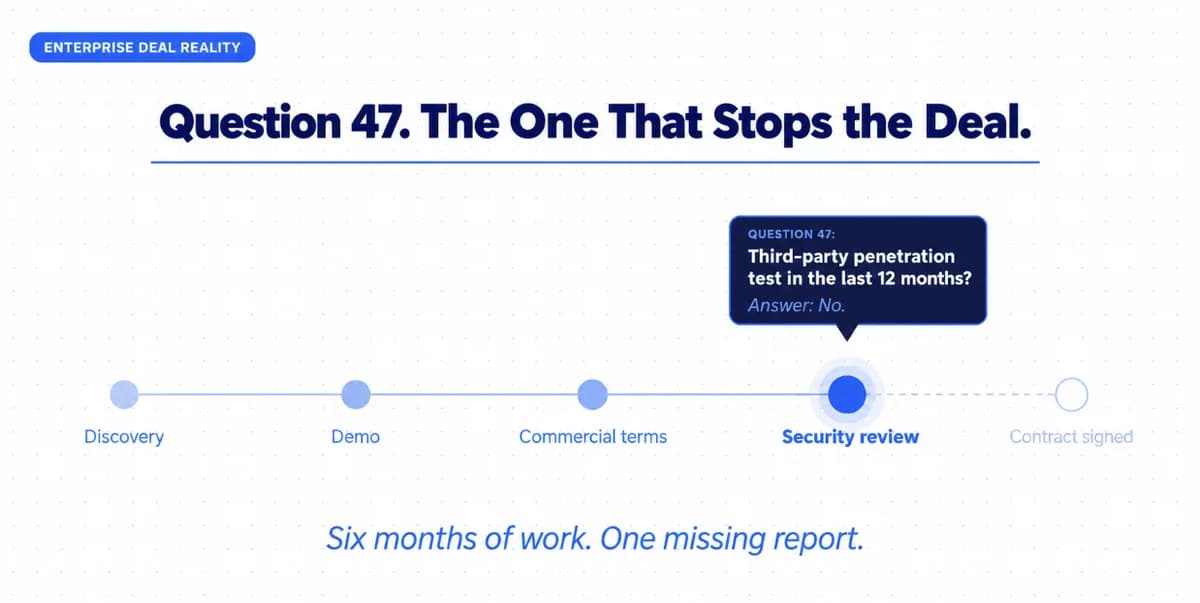
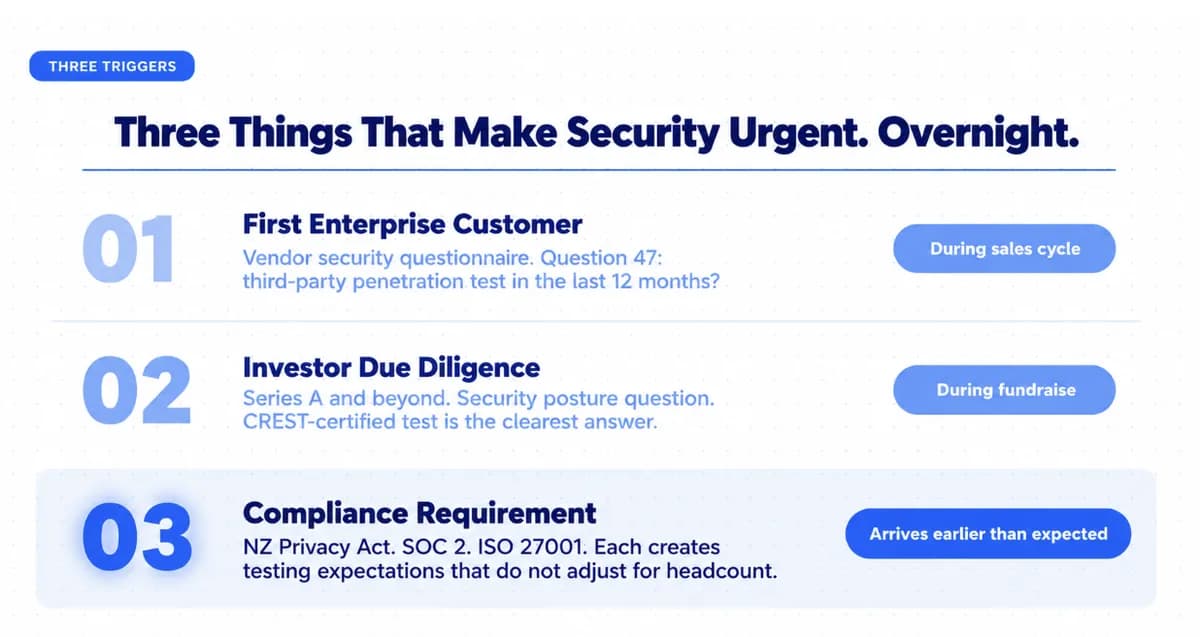
The first enterprise customer almost always asks for a penetration test report. It sits somewhere in the vendor security questionnaire, and it stops deals that took months to build. One missing document, one unanswered question, and the timeline slips by weeks or months.
Investors are asking about security posture more often during due diligence, especially at Series A and above. A CREST-certified penetration test is one of the clearest and most credible answers a founder can give. It shows the work has been done by an independently verified tester, not self-assessed.
And for founders building in fintech, healthtech, or SaaS that handles personal or sensitive data, compliance obligations arrive earlier than most expect. SOC 2, ISO 27001, and the New Zealand Privacy Act all create security testing expectations that do not adjust for headcount or runway.
Your Last Pentest Is Already Out of Date
Every week you ship without continuous testing is a week a vulnerability goes unseen. See what Capture The Bug finds in your first engagement.
What Security Testing Looks Like at the Startup Stage
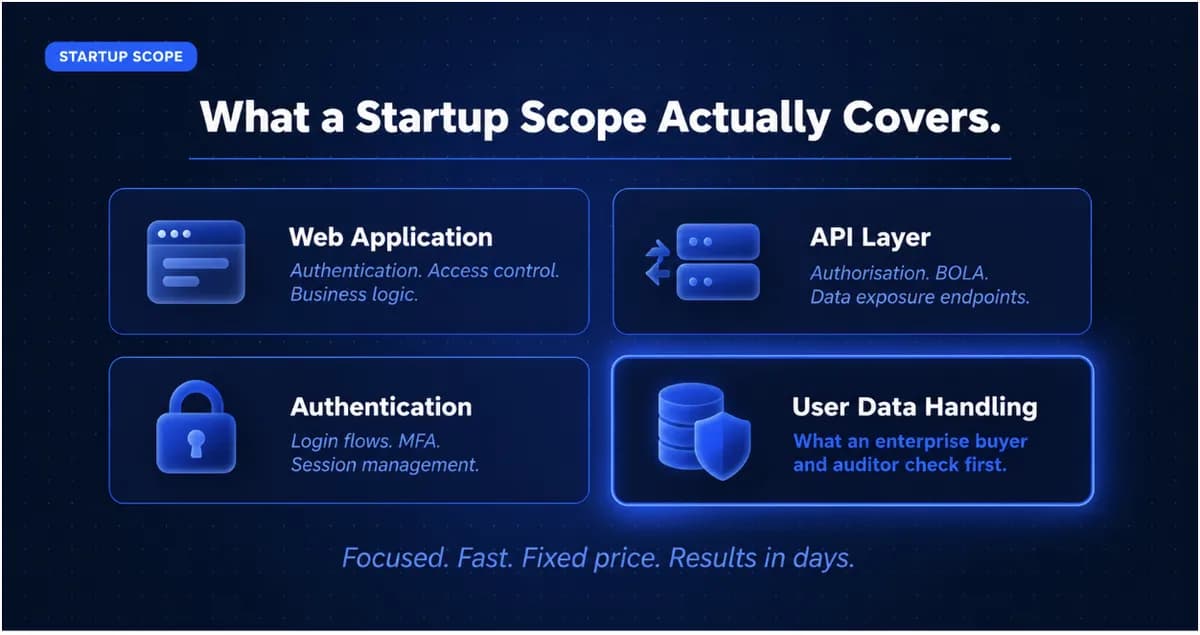
Most early-stage startups do not need the same scope as a large enterprise with thousands of endpoints and legacy infrastructure.
What they need is a focused test of the systems they are actually shipping. The web application. The API. The authentication layer. The user data they hold. That is the attack surface that matters to an enterprise buyer or a SOC 2 auditor, and it is the scope that produces useful findings for an engineering team of four or ten people.
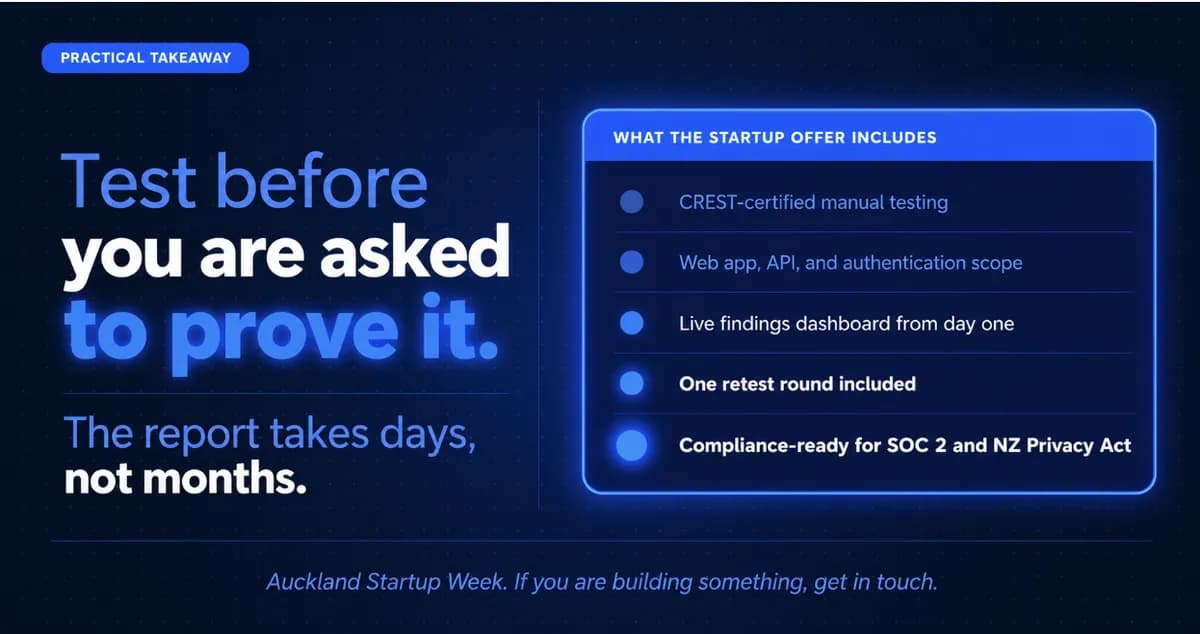
A well-scoped startup engagement covers what matters, produces a report that satisfies an auditor or enterprise buyer, and leaves the team with a clear list of what to fix. Then it confirms those fixes actually worked through a retest before the report is delivered.
That is what CREST-certified testing at the startup stage looks like. Not a six-figure enterprise engagement. A focused, fast, fixed-price test of the systems you have built so far.
Results arrive in days, not months. The report is compliance-ready for SOC 2, ISO 27001, and the New Zealand Privacy Act. Findings go live on a dashboard your team can see in real time. And one round of retesting is included so the report reflects what is actually fixed, not just what was found.
If You Are Building in New Zealand Right Now
Auckland Startup Week is a good moment to ask whether your security posture matches where you are taking the company, not just where you are today.
If you are preparing for your first enterprise customer, launching a new product feature, or heading toward a fundraise or certification, a penetration test is one of the clearest security signals you can add to the conversation.
We are expanding our startup-friendly offer to support more NZ teams through the Airtree and Ministry of Awesome partnerships. If you are building something and want to understand what a focused security test looks like at your stage, get in touch.
Learn how to prepare for your first enterprise security questionnaire in the guide to how known vulnerabilities still get exploited and what buyers look for before they sign.
And for a plain explanation of what the test actually produces, the guide to what happens after a penetration test covers the full evidence cycle from findings through to confirmed remediation.
Plan Your Annual Pentesting Strategy the Right Way
Learn how modern SaaS companies structure pentesting across the year to reduce risk, stay compliant, and avoid last-minute panic before audits.