
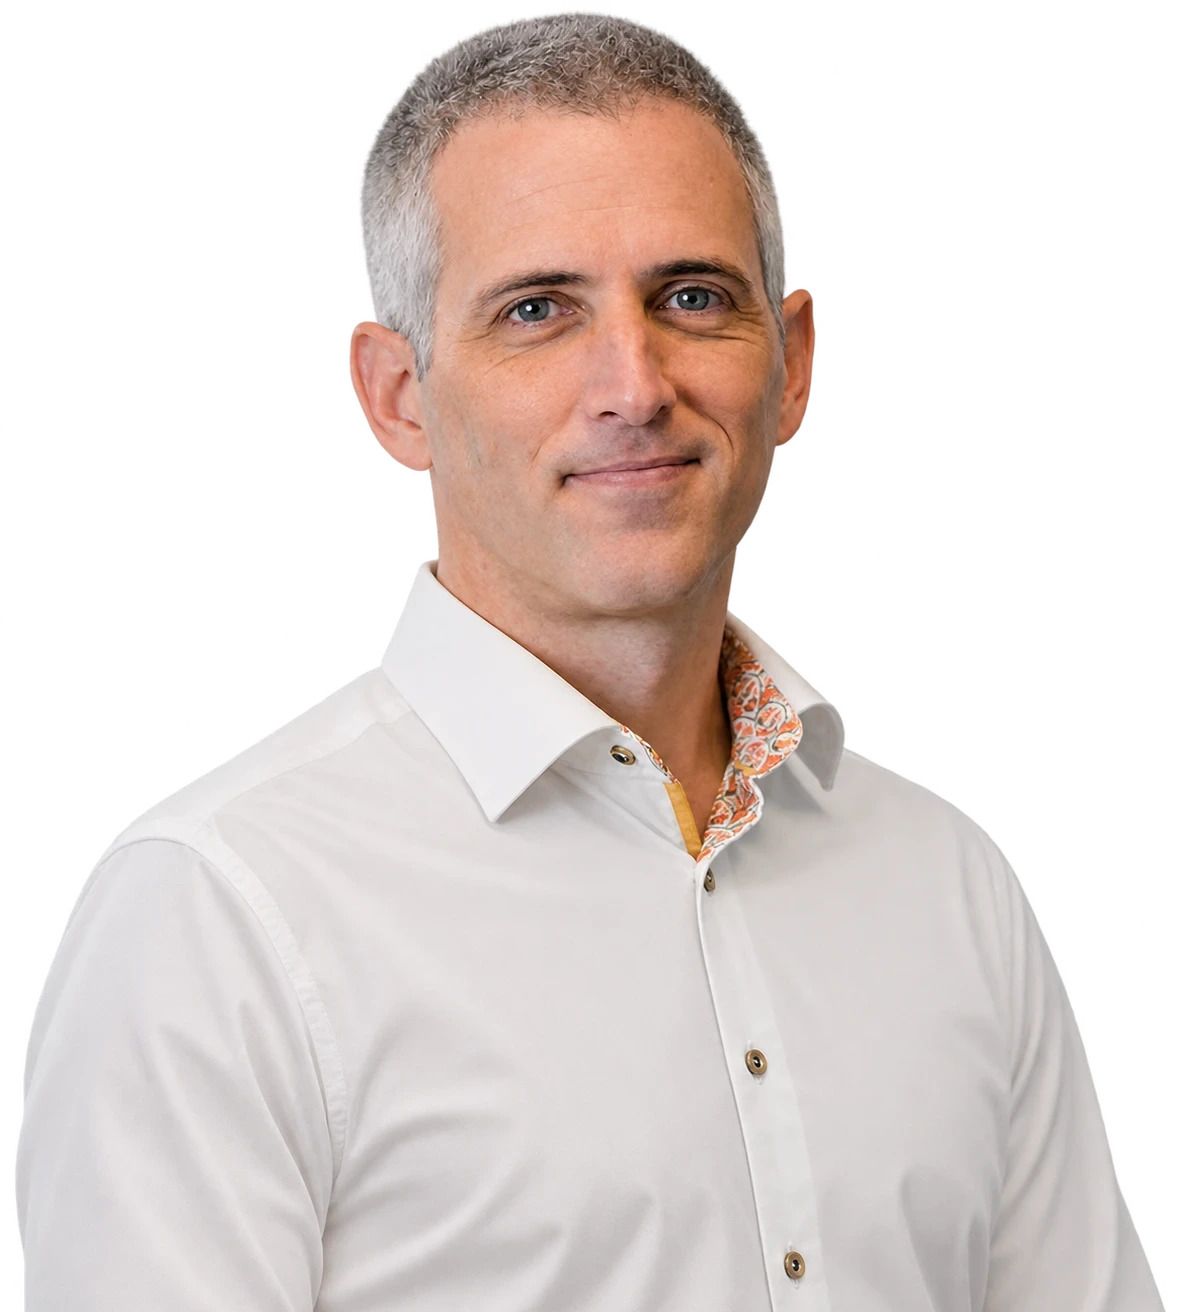
“We would highly recommend Capture The Bug to anyone who needs continuous assurance and speed without compromising depth.”
Jacques Labuschagne
Chief Technology Officer, PaySauce
Expert-led pentesting for applications, APIs, cloud and AI-powered apps. Uncover exploitable vulnerabilities, collaborate directly with testers and verify remediation through one platform.
Trusted by security and engineering teams at



“We would highly recommend Capture The Bug to anyone who needs continuous assurance and speed without compromising depth.”
Jacques Labuschagne
Chief Technology Officer, PaySauce
“Thanks to their continuous monitoring and clear communication, we’ve built a more resilient and security-aware development process.”
Nathan Taylor
Chief Operating Officer, Partly
“The platform made it easy to scope, schedule, and track the test in real time, no long email chains or delays.”
Shai Bhula
Chief Technology Officer, Whip Around
Each release can reshape your risk. Ongoing testing helps you spot new exposure, prioritise what counts and verify each fix.
New APIs, features and integrations can introduce exposure a single assessment may not cover.
Without regular testing, it can be hard to see what's covered and where exposure remains.
When findings sit outside engineering tools, ownership and progress become harder to follow.
Until a fix is retested, there's no evidence the risk is actually closed.
A disciplined, specialist-led process with clear visibility from kickoff to closure.
Talk to a Security ExpertAgree assets, objectives and boundaries with your assigned specialists.
Specialists combine a structured methodology with hands-on testing.
Each finding is checked by a specialist and supported by evidence.
Work through fixes with clear guidance and direct specialist access.
Request a retest within your engagement terms and record the result.
Manage scope, review findings and follow remediation in one place, from assessment to assurance.
Risk score
down from 72 last quarter
Open critical
Assets tested
Retest passed
#CTB-0139 · just now
New critical assigned
to J. Moreno · SLA 3 days
Our specialists assess AI agents, connected tools, data access and trust boundaries the way a real attacker would.
Explore AI Penetration TestingWhat we assess
Whether an AI agent can be pushed into running actions or tools it should not use.
How far a model or agent can reach into databases and sensitive business data.
Whether injected instructions in prompts or documents can change how the system behaves.
Where AI components meet your core systems, and where those boundaries can break down.

A Singapore HR-technology company moved from delayed, end-of-engagement reporting to expert-led PTaaS, with early findings, direct collaboration with the testers and Slack and Jira workflows.
 Telecommunications & technology
CREST-certified penetration testing for evolving technology platforms, with context-aware assessments, tailored reporting and direct collaboration with skilled pentesters.
 Security & compliance
Web and API testing across two customer portals began within 24 hours of sign-off, with evidence delivered on schedule.
Why Capture The Bug
Independent accreditation, recognised methodology and experienced specialists behind every engagement.
Every assessment is delivered within an agreed scope, with human-validated findings, specialist technical review and clear remediation evidence.
Accreditation
Capture The Bug holds CREST accreditation for penetration testing.
One of the first four companies in the world, and the first in New Zealand, to achieve CREST Security Testing of AI accreditation.
We have signed the CREST AI Charter for the responsible use of AI in security services.
Methodology
Testing aligned with OWASP ASVS, OWASP MASVS, the OWASP API Security Top 10 and the OWASP Top 10 for LLM Applications.
OWASP ASVS
Application Security Verification Standard
OWASP MASVS
Mobile Application Security Verification Standard
OWASP API Top 10
API Security Top 10
OWASP LLM Top 10
Top 10 for LLM Applications
Engagements are led by experienced security specialists, including researchers with published CVEs.
See how we handle credentials, customer data and security findings.
Connect validated findings with your engineering workflows, reducing manual handovers and keeping remediation visible.
 Vanta
Specialist testing for applications, APIs and AI, along with mobile, cloud and network environments.
Recurring expert assessments planned around your release cadence and changing security priorities.
Adversarial testing of LLM applications, AI agents, connected tools and the data they can reach.
Manual testing of authentication, roles, business logic and APIs, aligned with OWASP ASVS and the API Top 10.
iOS, Android and hybrid apps assessed statically and at runtime, in line with OWASP MASVS.
AWS, Azure, Google Cloud and network testing focused on the paths a real attacker would take.
Penetration testing evidence organised for SOC 2, ISO 27001, PCI DSS and HIPAA assurance programmes.
Both have a place. The right choice depends on how often your environment changes and what you need to prove.
Best for: a specific release, audit or customer requirement
Explore penetration testingBest for: teams that release often and need ongoing assurance
Explore continuous penetration testingNot sure which fits? Talk to a Security Expert
Talk to a specialist about one-off testing or an ongoing programme, scoped to your applications, environment and security goals.
Active Findings
Last updated 2 hours ago
SQL Injection in User Authentication
VULN-042
Stored XSS in Comment Field
VULN-041
Insecure Direct Object Reference (IDOR)
VULN-040
Missing Rate Limiting on Login
VULN-039