Subscriber Account Takeover
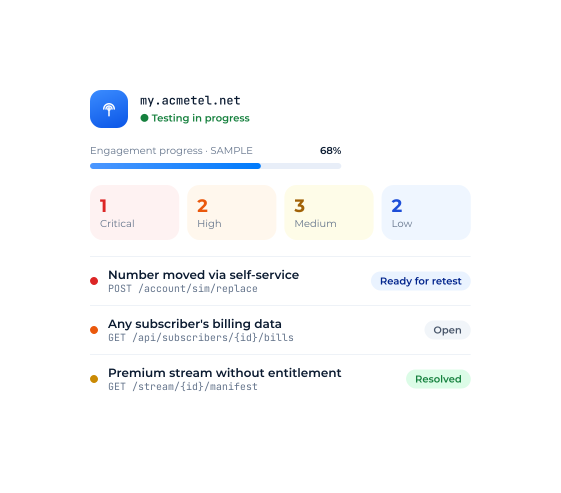
Weak account recovery controls enabling unauthorised access to subscriber services.
Expert-led testing for telecoms platforms, subscriber systems and network infra, with validated findings and verified remediation through one connected platform.

“Three months into our journey with CTB, we are impressed by the responsiveness of their team and the immediate insights from CTB's App. We can now launch pen-test programs on-demand and start seeing results within a couple of days.”
Independent Assurance
 CREST-Accredited
 CREST Security Testing of AI
- Telecom and Media Risks
Four security weaknesses affecting subscriber information, access and critical services.
Weak account recovery controls enabling unauthorised access to subscriber services.
Insecure APIs exposing customer records, usage information and billing data.
Weak authorisation allowing access to restricted services without valid permissions.
Internet-facing management interfaces and services exposing critical network infrastructure.
- What We Test
Customer portals and billing systems.
Learn moreSubscriber, provisioning and billing APIs.
Learn moreSubscriber self-service and account apps.
Learn moreExternal and internal network services.
Learn moreCloud infrastructure supporting subscriber services.
Learn moreAI customer support and service management assistants.
Learn more- How We Work
Expert-led testing with live findings, direct collaboration and verified remediation support.
Agree network assets, applications, access and testing boundaries.
Agreed ScopeSpecialists assess networks and systems for exploitable weaknesses.
Live FindingsReview validated findings with evidence, severity and remediation guidance.
Validated FindingsWork with our specialists to address vulnerabilities across your infrastructure.
Fix GuidanceVerify fixes within agreed engagement terms.
Verified FixDiscuss your testing requirements and priorities with our security specialists.
- Assurance & Evidence
SOCI Act
Evidence supporting applicable Australian critical infrastructure risk obligations.
TICSA
Evidence supporting applicable New Zealand telecommunications security obligations.
ISO 27001
Technical evidence supporting information security management controls.
Privacy Act
Testing evidence supporting privacy safeguards for subscriber and customer information.
Validated findings and remediation evidence support customer assurance, security reviews and relevant regulatory obligations.
Depending on scope, testing may include customer-facing applications, APIs, internal or external infrastructure, cloud environments, administrative portals and other systems that support telecommunications services. Testing should focus on the systems and attack paths that present the greatest business risk.
Yes. Capture The Bug provides penetration testing across web applications, APIs, mobile, cloud, network and infrastructure environments, allowing organisations to assess multiple parts of their attack surface through one testing relationship.
Authenticated testing may require privileged test accounts, API credentials or other sensitive access. Capture The Bug provides a secure Credential Vault and MFA-protected platform access so sensitive testing information can be handled within the engagement workflow rather than relying on informal credential sharing.
Validated findings can be made available through the Capture The Bug platform while testing is underway, giving security and engineering teams visibility before the final report and allowing remediation work to begin earlier where appropriate.
Yes. Your security and engineering teams can work directly with the specialists performing the assessment to clarify findings, discuss evidence and remediation, and coordinate retesting.
Not necessarily. A one-off pentest may be appropriate for a defined system or assurance requirement. However, organisations with frequently changing applications, APIs, infrastructure and integrations may benefit from testing around material changes rather than relying only on a fixed annual testing cycle.
Expert-led penetration testing for critical networks and services.