Health and Incident Records
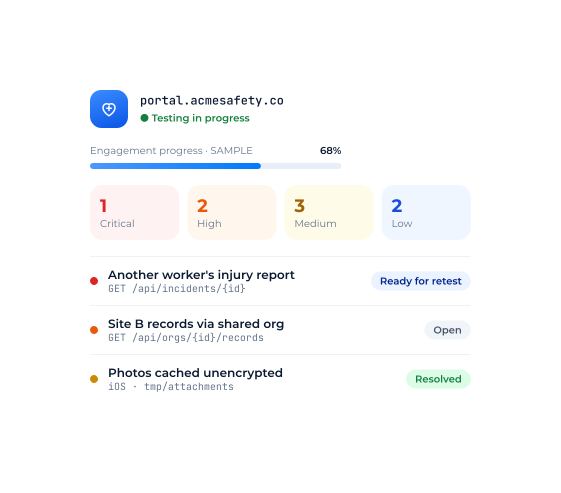
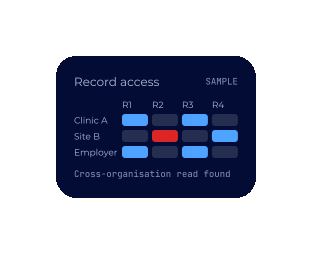
Broken record access exposes another worker's sensitive health information.
Expert-led pentesting for incident management, employee records and safety applications, with validated findings and verified remediation through our PTaaS platform.

“Capture The Bug has made penetration testing easier to manage alongside our development work. Having direct access to their specialists, clear visibility of findings and a straightforward remediation process helps us maintain confidence as our platform evolves.”
Independent Assurance
 CREST-Accredited Testing
 CREST Security Testing of AI
- Health and Safety Risks
Four critical security weaknesses threatening sensitive workplace health and safety information.
Broken record access exposes another worker's sensitive health information.
Insufficient tenant isolation exposes records across organisations using shared platforms.
Insecure mobile storage exposes incident photos and sensitive workplace records.
Excessive integration permissions expose sensitive information beyond intended access.
- What We Test
Incident platforms and employee portals.
Learn moreIncident records and integration APIs.
Learn moreWorkplace safety and reporting apps.
Learn moreCloud platforms protecting sensitive workplace safety data.
Learn moreWorkplace safety and reporting assistants.
Learn moreNetworks, exposed services and permissions.
Learn more- How We Work
Expert-led testing, live findings and remediation tracking through one connected platform.
Agree applications, user roles, sensitive records and testing boundaries.
Agreed ScopeSpecialists assess access controls, APIs and exploitable vulnerabilities.
Live FindingsAccess validated findings with evidence, severity and remediation guidance.
Validated FindingsCollaborate with specialists to address security risks across your platform.
Fix GuidanceVerify remediation within your agreed engagement terms.
Verified FixesDiscuss your security requirements with our specialists today.
- Assurance & Evidence
ISO 27001
Technical evidence supporting organisational information security policies and controls.
OWASP Application Security Verification Standard
Structured application security testing guidance.
Privacy Act
Evidence supporting privacy safeguards for sensitive worker and incident personal information.
SOC 2
Validated findings supporting security controls and assurance reviews.
Validated findings and retesting evidence support customer assurance, security reviews and relevant compliance requirements.
Yes. We agree test environments, accounts and data handling safeguards before starting any assessment.
Yes. Our validated findings and retesting evidence support customer reviews and security assurance programmes.
Yes. We assess tenant isolation, permissions and access controls to identify cross-organisation data exposure.
Yes. We test field applications for insecure storage, authentication weaknesses and unauthorised data access.
Once fixes are implemented, our specialists retest affected functionality and document outcomes within scope.
Expert-led penetration testing for sensitive workplace data and applications.